Aakash is deployed as a Security Analyst, conducting deep reconnaissance across digital attack surfaces, identifying exploitable weaknesses, and strengthening organizational security posture against evolving threats. Through hands-on assessments, he continuously works to reduce attack surfaces and enhance the resilience of critical digital infrastructure.
Operating with a combat-ready foundation in Network Security, Web Application Security, and Vulnerability Assessment & Penetration Testing (VAPT), he specializes in uncovering security gaps through systematic recon, threat modeling, and adversarial emulation. His operational methodology aligns with established cyber warfare doctrines, leveraging OWASP and MITRE ATT&CK frameworks to map, analyze, and emulate real-world adversary tactics, techniques, and procedures (TTPs).
His three-year tenure in the National Cadet Corps (NCC) served as a force multiplier in shaping the discipline and operational mindset that he brings to the cyber domain. The training reinforced mission-focused execution, situational awareness, leadership under pressure, teamwork, and unwavering accountability—qualities that directly enhance performance during threat-hunting operations, incident response, and security assessments. NCC ingrained the principles of preparedness, adaptability, and continuous readiness, which remain fundamental to every cyber mission he undertakes.
His operational trajectory is driven by relentless analytical curiosity, continuous learning, and strict adherence to ethical engagement protocols. To maintain peak operational readiness and sharpen his technical capabilities, he regularly conducts live-fire cyber exercises and adversarial simulation drills. Every engagement is treated as a training ground to refine recon capabilities, strengthen offensive tradecraft, and enhance defensive effectiveness against modern cyber threats.
Security Doctrine
Establish context before drawing conclusions.
Corroborate information using independent, credible sources.
Distinguish verified facts from analytical inferences.
Translate collected information into relevant, evidence-based security insights.
Evaluate systems from an adversary’s perspective.
Challenge assumptions surrounding authentication, authorization, and trust boundaries.
Examine how individual weaknesses may combine to create broader attack paths.
Use controlled, authorized testing to establish realistic security impact.
Substantiate findings before drawing conclusions.
Verify observed behavior through reproducible testing wherever feasible.
Document testing limitations and distinguish confirmed impact from potential risk.
Assign severity based on evidence, exploitability, and realistic consequences.
Conduct security work with precision, accountability, and professional integrity.
Operate within explicitly authorized scopes and defined testing boundaries.
Apply controlled methodologies and maintain clear, accurate documentation.
Handle sensitive information responsibly and follow applicable disclosure requirements.
Experience
Confidential
Security Analyst
Mar 2026 – Present
Performed manual web application and API penetration testing using Burp Suite, identifying and validating vulnerabilities including IDOR/BOLA, BFLA, CSRF, and sensitive data exposure.
Assessed APIs against the OWASP API Security Top 10 (2023), with a focus on authentication and authorization controls, JWT security, mass assignment, excessive data exposure, and rate limiting.
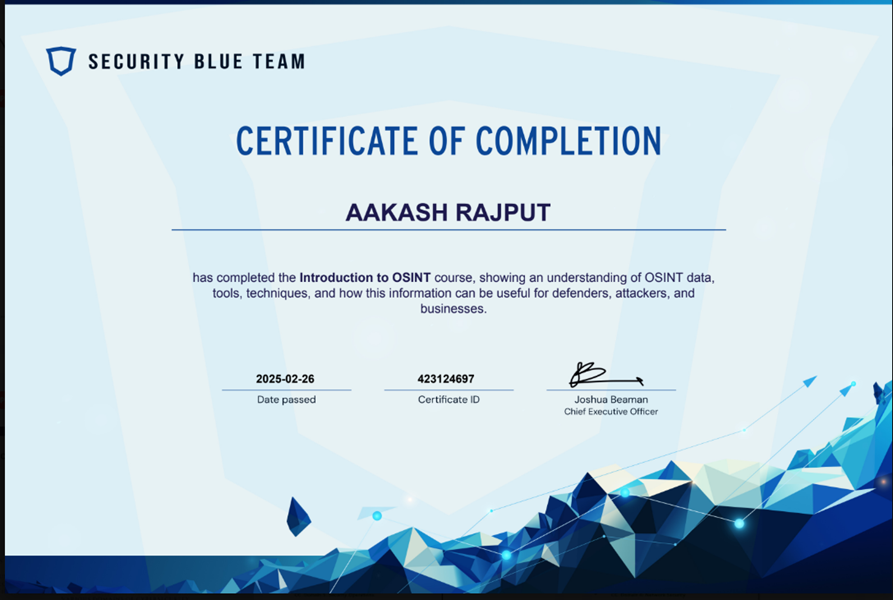
Conducted OSINT-driven reconnaissance and attack-surface mapping, including subdomain enumeration, exposed-service identification, credential-exposure checks, and employee digital-footprint analysis prior to security testing.
Supported social engineering and phishing assessments through pretext development, simulated campaigns, and security-awareness recommendations.
Documented and validated 50+ security findings, collaborating with development teams to verify remediation and closure.
Version Systems Pvt. Ltd.
Professional Auditor
📅 Nov 2025 – Feb 2026
Supported ISO 27001 compliance activities, including evidence collection, policy review, control assessment, and risk assessment.
Conducted risk-based internal audits aligned with ISO 9001:2015 across software development and support functions, identifying non-conformities, control gaps, and process-improvement opportunities.
Coordinated with cross-functional teams on audit readiness, corrective-action tracking, and closure verification within defined timelines.
Education
B. Tech in CSE
Maharishi University of Information Technology
📅 2020 – 2024
NCC — National Cadet Corps
ARMY Wing, Uttar Pradesh Directorate
📅 2020 – 2023
Completed three years of NCC training, developing military-style discipline, accountability, and a strong sense of duty.
Selected for the Advanced Leadership Camp (ALC), where I represented and led my battalion at the national level, demonstrating leadership, coordination, and team management.
Strengthened physical endurance, mental resilience, and composure through structured cadet training and activities.
Developed decision-making, adaptability, and time-management skills while working in disciplined, team-oriented environments.
Cultivated a mission-oriented mindset, emphasizing teamwork, responsibility, and commitment to collective objectives.
// Services
Web Application Penetration Testing
Web applications are the primary attack surface for most organizations. My web application penetration tests go far beyond automated scanning — I manually test for complex vulnerabilities, including business logic flaws, multi-step authentication bypasses, race conditions, and chained attack scenarios that automated tools consistently miss.
SQL InjectionXSSCSRFSSRFXXEOWASP Top 10
What’s Covered
OWASP Top 10 (2025) — comprehensive coverage of broken access control (including SSRF), security misconfiguration, software supply chain failures, cryptographic failures, injection (including XSS), insecure design, authentication failures, software and data integrity failures, security logging and alerting failures, and mishandling of exceptional conditions
Business logic testing — workflow manipulation, price tampering, privilege escalation through application logic
Detailed report with executive summary, technical findings with proof-of-concept, risk ratings (CVSS), remediation recommendations, and a remediation verification retest.
Vulnerability Research
Beyond standard penetration testing, I conduct deep vulnerability research aimed at discovering zero-day vulnerabilities and novel attack techniques.
Zero-day ResearchAttack Surface Analysis
What’s Covered
Zero-day research — discovering previously unknown vulnerabilities in commercial and open-source software
Attack surface analysis — comprehensive mapping of an organization’s exposure across all digital assets
API Security Testing
APIs power modern applications and are increasingly targeted by attackers. I test APIs for authorization flaws, injection vulnerabilities, rate-limiting issues, and data exposure that could compromise your backend systems and user data.
API TestingAuthentication & JWT SecurityMass AssignmentExcessive Data ExposureInsufficient Rate Limiting
What’s Covered
BOLA (Broken Object Level Authorization) — testing for IDOR vulnerabilities across all API endpoints
BFLA (Broken Function Level Authorization) — verifying role-based access controls on sensitive operations
Mass assignment — testing for unintended parameter binding that could modify protected fields
Excessive data exposure — identifying responses that return more data than the client needs, including sensitive object properties
Insufficient rate limiting & resource consumption — denial of service through API abuse, pagination bypass, and brute-force exposure
Injection attacks — SQL injection, NoSQL injection, and command injection via API parameters
Authentication & JWT security — JWT analysis, OAuth flow testing, API key leakage, and token lifetime and rotation
Tools Used
Burp Suite, Postman, custom Python/Go scripts, Nuclei, ffuf, and wfuzz
Deliverables
API security assessment report with OWASP API Security Top 10 mapping, endpoint-level findings, and API-specific remediation recommendations.
Testing Tools
Good testing is a mix of the right tools and the judgment to know when they are wrong. I use industry-standard tooling for discovery, scanning, and exploit validation, then reproduce every automated result by hand before it goes anywhere near a report.
Burp SuiteNmapMetasploitOWASP ZAPWiresharkSQLmapNucleiNiktoffufGobusterHydraHashcatJohn the RipperImpacketNetExecBloodHoundResponder
What’s Covered
Intercepting proxy & manual testing — Burp Suite for request tampering, session and access-control testing, and replaying attacks step by step
Network discovery & enumeration — Nmap for host, port, and service mapping, version detection and scripted checks
Exploitation framework — Metasploit for safely validating the exploitability of confirmed issues, strictly within the agreed scope
Automated scanning — OWASP ZAP, Nuclei, and Nikto for fast coverage of known issues and misconfigurations
Packet analysis — Wireshark for inspecting traffic, spotting cleartext data and understanding protocol behavior
SQL injection testing — SQLmap to confirm and demonstrate injection flaws found during manual testing
Content & parameter discovery — ffuf and Gobuster for directory, file, virtual-host, and parameter fuzzing
Password & credential testing — Hydra for authorized online credential testing; Hashcat and John the Ripper for offline password-strength auditing of recovered hashes
Internal network & Active Directory — Impacket, NetExec, BloodHound, and Responder for enumerating domains, mapping privilege paths, and validating credential-relay risks
Approach
Scanners find candidates; people confirm vulnerabilities. Every finding is reproduced manually and documented with evidence, reproduction steps, and the exact scope it applies to.
OSINT & Reconnaissance
Open-source intelligence is where most real-world attacks begin — and where a defender can learn the most about their own exposure. I map what is publicly discoverable about an organization, from domains and infrastructure to people and leaked data, so you can see your footprint the way an attacker would.
Domain & infrastructure recon — subdomain enumeration, DNS and WHOIS records, certificate transparency, and internet-exposed services
Search-engine intelligence — Google dorking to find exposed files, admin panels, and sensitive information indexed by mistake
People & social footprint — employee and role mapping, username correlation, and social-media exposure that could feed social engineering
Email & credential exposure — harvested addresses and publicly reported breach exposure that could enable phishing or account takeover
Attack surface mapping — correlating everything into one picture of what an attacker can learn before sending a single packet
Rules of Engagement
Passive, publicly available sources only, within a scope and legal boundaries agreed upon in writing beforehand.
Deliverables
Footprint report with an asset inventory, exposure findings ranked by risk, the source for every item, and recommendations to shrink your public attack surface.
Frameworks & Standards
Findings are most useful when they can be tied to the standards your business answers to. I align testing and recommendations with recognized frameworks, so a technical report doubles as evidence for your security and compliance program.
OWASP Top 10CWE/CVEISO 27001ISO 9001:2015DPDPSOC 2
What’s Covered
OWASP Top 10 (2025) — the baseline for classifying web application risks, alongside the OWASP API Security Top 10 (2023) for APIs
CWE / CVE — classifying weaknesses and referencing publicly known vulnerabilities consistently
ISO 27001 — relating findings to the relevant Annex A controls of your information security management system
ISO 9001:2015 — following quality-management principles for consistent, documented, and continually improved engagement processes and reporting
SOC 2 — relating findings to the Trust Services Criteria, especially security, to support audit readiness
DPDP — highlighting personal-data exposure and safeguards relevant to India’s Digital Personal Data Protection Act
Deliverables
Findings mapped to the relevant framework controls, with prioritized remediation guidance. This is technical assurance and readiness support — not a formal audit or certification.
Engagement Process
Every engagement follows a structured process, so scope, effort, and delivery stay clear from the first call to the final retest.
01
Scoping Call
We talk through your goals, systems, and concerns, then agree on the targets, rules of engagement, methodology and timeline.
02
Proposal & Authorization
You receive a clear proposal. Testing only begins once the scope is signed off and written authorization — plus an NDA, if needed — is in place.
03
Testing
Hands-on manual testing backed by trusted tooling, following recognized methodologies. You get progress updates throughout, and anything critical is flagged straight away.
04
Reporting
A clear report with an executive summary, technical findings with proof-of-concept and evidence, severity ratings, and prioritized fixes.
05
Remediation Support
I stay available to explain the findings and help your team fix them, followed by a retest to confirm the issues are actually closed.
Ready to Start an Engagement?
Tell me what you need tested — the target, rough scope, timeline, and whether an NDA is required — and I’ll get back to you within 24–48 hours.
Engagements: Engagement 1 — Apr 2026 to Jun 2026 • Engagement 2 — Jul 2026 to Sep 2026
Category: Professional Experience • Security Assessment
Focus Areas: Web Application Penetration Testing • API Security • OSINT • Social Engineering
Overview: Contributed to authorized security assessments spanning web applications, APIs, external attack-surface reconnaissance, and social engineering. The work focused on identifying and validating security weaknesses, evaluating their potential impact, and supporting remediation through evidence-based reporting and verification.
Scope of Work & Contributions:
OSINT & Attack-Surface Reconnaissance
Conducted OSINT-driven reconnaissance, including subdomain enumeration, exposed-service identification, credential-exposure checks, and employee digital-footprint analysis.
Used reconnaissance findings to shape the assessment approach and identify areas requiring further security investigation.
Web Application & API Penetration Testing
Performed manual web application and API penetration testing using Burp Suite, identifying and validating issues involving IDOR/BOLA, Broken Function Level Authorization (BFLA), Cross-Site Request Forgery (CSRF), and sensitive data exposure.
Assessed API security controls against the OWASP API Security Top 10 (2023), focusing on authentication, authorization, JWT security, mass assignment, excessive data exposure, and rate limiting.
Social Engineering & Phishing Assessments
Supported social engineering assessments through pretext development and simulated phishing campaigns.
Contributed security-awareness recommendations to address identified human-layer risks and improve organizational preparedness.
Risk Assessment & Remediation Validation
Documented and validated 50+ security findings across assessments.
Collaborated with development teams to verify remediation efforts and confirm finding closure.
Assessment Approach: Applied a structured methodology combining reconnaissance, manual security testing, evidence collection, risk classification, and remediation verification, with an emphasis on defensible findings, actionable recommendations, and responsible handling of sensitive information.
Tools & Frameworks: Burp Suite • OWASP API Security Top 10 (2023)
Status: Completed
Industrial Intrusion CTF | TryHackMe
Rank 781 · OT / ICS Red Team CTF
📅 Jun 2025
Overview: Competed in TryHackMe’s Industrial Intrusion CTF (27–29 June 2025), an Operational Technology (OT) and Industrial Control Systems (ICS)-themed competition open to all participants, played in teams of up to five.
Scenario: Played as a hired red-team specialist investigating a compromised water-control facility, where an attacker had left a hidden second-stage implant reachable through overlooked OT backdoors and a compromised web portal.
Achievement: Finished at rank 781 on the scoreboard with 180 points.
Achievement: Gained hands-on exposure to industrial-environment attack surfaces and to how classic IT techniques carry over into OT networks.
Skills: OT / ICS Security • Enumeration • Red Teaming
Overview: Competed in TryHackMe’s Hackfinity Battle 2025, a global student-focused CTF held online from 17–20 March 2025, with teams of up to five members.
Achievement: Secured scoreboard rank 24 in a field of 4,300+ teams and 24,000+ participants worldwide.
Achievement: Earned 1,665 points by completing 44 tasks across multiple cybersecurity domains.
Achievement: Applied analytical reasoning and hands-on problem-solving across a four-day competition window.
Overview: A single-page, self-built reference that consolidates the commands, flags, and workflows for 40+ security tools into one fast, searchable interface — built to speed up day-to-day offensive, defensive, and OSINT work and to double as a structured study aid.
Category: Personal Project • Security Reference • Web
Coverage: 40+ tools • 330+ commands • 6 categories — Offensive, Defensive, OSINT, Social Engineering, Forensics / Malware, and AI & ML Security.
Focus Areas: Reconnaissance • Exploitation • Password Attacks • Web & API Testing • OSINT • Social Engineering • Digital Forensics
Highlights: Instant client-side search across every command • one-click copy buttons • dark / light / system themes • category quick-navigation • fully mobile-responsive layout.
Beyond Commands: Each section pairs raw syntax with tool methodology, practical tips, and authorization / legal notes — including an end-to-end Social Engineering workflow spanning reconnaissance, phishing, vishing / smishing, physical, and defensive layers.
Overview: Competed in the multi-domain Cybersecurity Hackathon CTF organized by the Data Security Council of India (DSCI) & EY at the 19th NASSCOM-DSCI Annual Information Security Summit (AISS) 2024, held 04–06 December 2024.
Achievement: Ranked in the top 40 of 240 participants — roughly the top 17% of the field.
Achievement: Solved challenges across web exploitation, digital forensics, and OSINT.
Achievement: Applied analytical reasoning and hands-on problem-solving under competition time pressure.
Tools: Burp Suite • Autopsy • theHarvester • Browser Web Inspector
Cybersecurity demands continuous adaptation, disciplined practice, and a willingness to challenge existing knowledge. My development approach focuses on strengthening technical depth, refining investigative judgment, and translating theoretical concepts into practical security skills.
Structured Technical Learning: Continuously develop knowledge of web application security, API security, authentication, authorization, and HTTP fundamentals.
Practical Skill Development: Reinforce concepts through TryHackMe labs, CTF challenges, and controlled security testing environments.
Research & Analytical Reasoning: Study emerging vulnerabilities, security advisories, attack techniques, and remediation approaches to understand the underlying causes and practical implications of security weaknesses.
Independent Technical Competence: Strengthen the ability to investigate, reproduce, analyze, and explain security findings through first-principles reasoning rather than relying solely on automated tools or external guidance.
Continuous Evaluation & Improvement: Review testing methodologies, assess knowledge gaps, and refine technical approaches through hands-on practice, evidence-based analysis, and lessons learned.
Contact Information
Got a bug bounty tip, a pentest or OSINT engagement, a CTF team invite, or a role to talk about? Fill out the form or reach me through any of the channels below.
Response time: Usually within 24–48 hours.
NDA: Available upon request before engagement.
Urgent? Start your message with “URGENT” for security matters.


 -->
 -->
 -->
 -->
 -->